Content Credentials for Designers: What They Prove and What They Don’t
Content Credentials can document an asset’s origin, edits, and AI involvement, but they do not prove truth or usage rights. Learn how to use them in a practical client workflow.
 Written by HiveGlyph
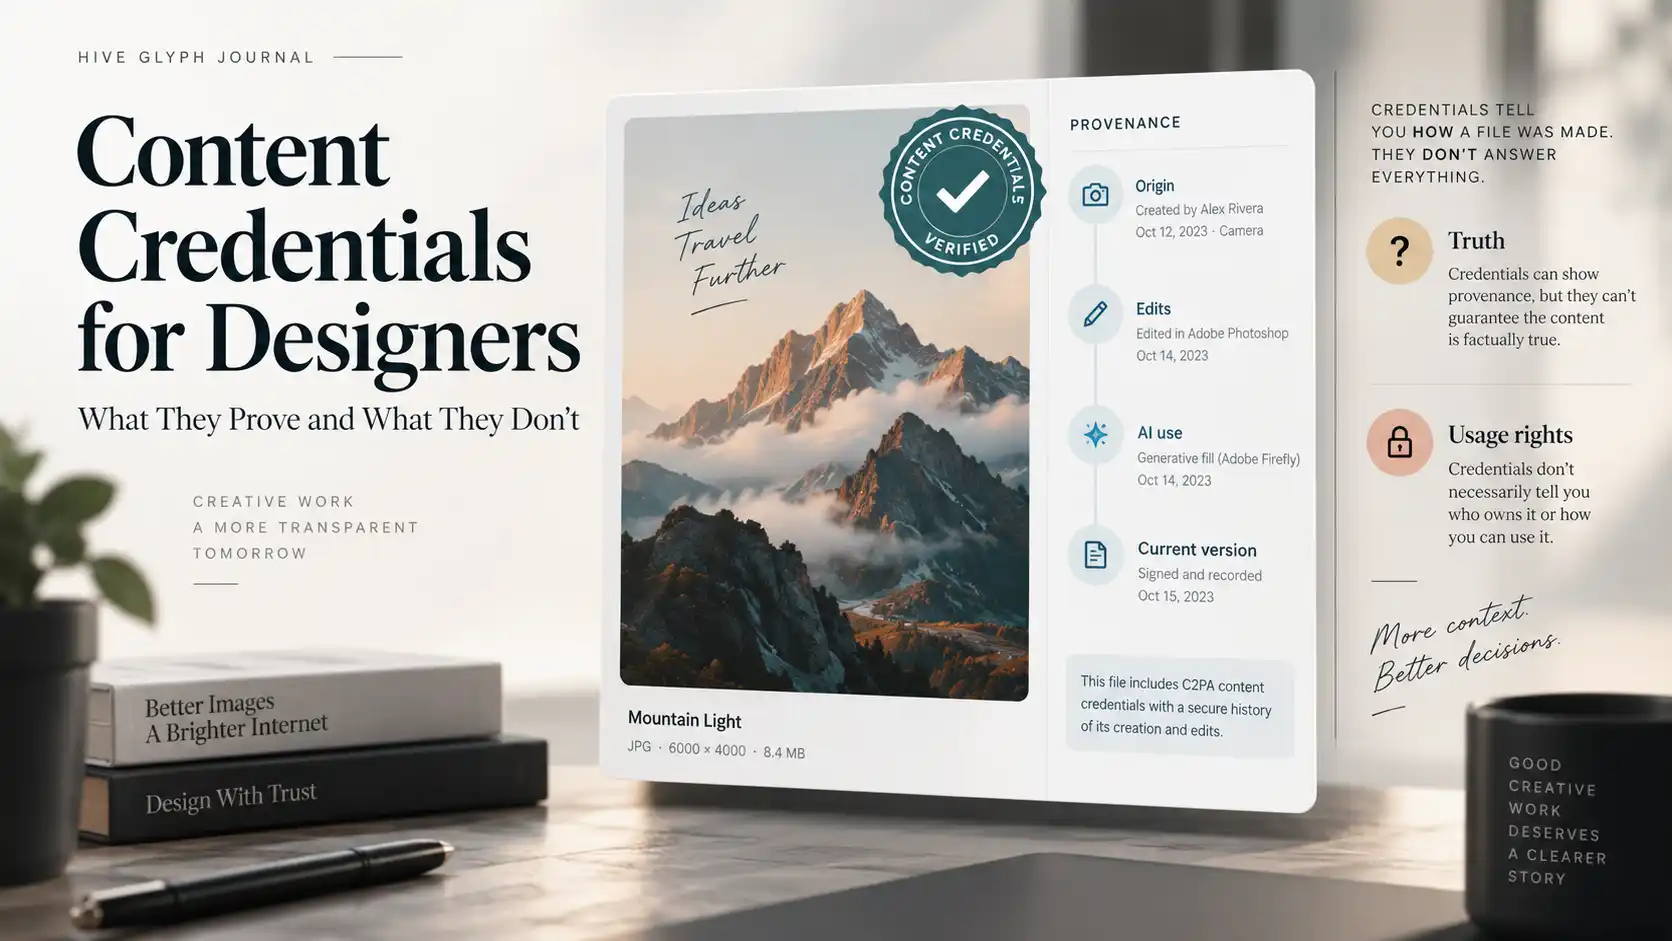
A client asks whether an image was generated by AI. The designer sends a screenshot of the layers panel. Another designer adds a note in the filename. Both gestures may be sincere, but neither gives the recipient a reliable way to check what happened to the actual exported file.
Content Credentials offer a more structured answer. They can attach signed provenance information to digital content, including details about its origin, edits, and use of generative AI. Yet they are often described too broadly, as though a credential proves that an image is true, legally safe, or entirely human-made.
It does not. For a working designer, the useful question is narrower. What can a Content Credential verify, where can the record break, and what other information still needs to accompany a client handoff?
Content Credentials record provenance, not creative purity
Content Credentials are based on the C2PA standard, developed by the Coalition for Content Provenance and Authenticity. The standard calls the attached record a C2PA Manifest. It can contain statements about where an asset came from, how it was modified, which tools were involved, and whether an AI system performed an action.
The record is cryptographically bound to the asset and digitally signed. That allows a compatible verifier to check whether the credential and the associated file have been altered since the manifest was created. The C2PA explainer describes this as tamper-evident provenance rather than a judgment about whether the content is good, bad, accurate, or misleading.
That distinction matters. A valid credential can help establish that a particular signer attached a particular history to a particular asset. It does not certify the artistic quality of the work. It also does not turn an unknown source into a trustworthy one.
Adobe’s current Content Credentials overview, updated on 25 August 2026, describes the system as a digital nutrition label for content. Adobe lists Photoshop, Lightroom, Adobe Stock, and Premiere among the supported applications and explains that credentials can include creator information and details about whether content was captured, edited, or generated with AI.
What a valid credential can tell you
A viewer using a compatible inspection tool may be able to see the signer, the application or device involved, declared editing actions, and whether generative AI was recorded in the workflow. The exact information depends on what the creator, device, and software chose to include.
For design teams, the most useful signals usually fall into three groups.
- Origin. The record may identify the tool, device, publisher, or creator associated with an asset.
- Process. It may describe edits or ingredients added during production, including actions attributed to AI systems.
- Integrity. A verifier can check whether the signed asset and its credential still match.
These signals are valuable during review. A designer receiving campaign photography can inspect available provenance instead of relying only on a filename or email description. A client receiving an AI-assisted composition can see a declared production history rather than a vague assurance that AI was used “only a little.”
What Content Credentials do not prove
The limitations are as important as the benefits. C2PA states that provenance alone cannot determine whether an image depicts something true, accurate, or factual. A signed file can contain a staged photograph, a fictional illustration, or a misleading caption. The signature protects the record from unnoticed alteration. It does not investigate the subject.
| Credential may help verify | Credential does not automatically prove |
|---|---|
| The signed file matches the attached manifest | The depicted event happened as presented |
| A declared tool or process was recorded | Every earlier edit is included |
| Generative AI use was declared by a supported workflow | No AI was used when the record is absent |
| A signer is associated with the credential | The signer owns every copyright or license |
| The provenance record is tamper-evident | The file is approved for every commercial use |
Absence is not proof of deception either. C2PA adoption is optional, and many legitimate files were created before compatible tools became available. Some applications do not write credentials. A conversion or export can also remove the metadata. The C2PA documentation explicitly notes that provenance may be incomplete and that metadata can be removed.
Creator identity is another separate issue. The core standard focuses on provenance and authenticity of the asset, while identity information may be added through extensions. A credential with no personal name can still contain useful process information. Conversely, a displayed name should be evaluated in the context of how it was verified.
Content Credentials are not a license
This is the easiest mistake to make during asset handoff. Provenance and permission answer different questions.
A credential can tell you something about the history of a file. A license tells you what you are allowed to do with it. C2PA specifically distinguishes Content Credentials from digital rights management. The standard does not restrict access or impose usage limits.
If a stock image has a valid credential, the client still needs the correct stock license. If a commissioned illustrator attaches attribution, the agreement still needs to define usage rights. If a font appears inside the artwork, the relevant desktop, web, app, or other license still needs to match the project. Our creative asset licensing workflow explains how to keep those approvals traceable.
Keep the documents separate. Do not paste licensing claims into a provenance note unless they have been checked against the actual agreement. For a broader handoff review, use our guide to checking editable design files before client delivery.
Build provenance checks into the workflow
Content Credentials are most useful when they are checked at defined points, not discovered after a client raises a concern.
Inspect incoming assets
When an image arrives from a photographer, stock provider, collaborator, or AI service, keep the original download. Inspect any available credential before placing the file into a larger composition. The public Content Credentials Verify tool can display supported provenance records without requiring the recipient to interpret raw metadata. Record the source URL, purchase receipt, license, and approval separately. Provenance can strengthen that record, but it should not replace it.
Preserve a clean master
Keep an untouched copy of the received asset and a layered working file. Repeated exports make it harder to understand which version still carries the credential. Clear version names and a short source log remain useful even when the metadata works perfectly.
Be specific about AI involvement
“AI-assisted” can mean many things. A designer might use generative fill to extend a background, create an entire image from a prompt, or use an automated removal tool on a photograph. Where the software records those actions, the credential can provide structured context. The handoff note should still explain the important creative decision in plain language.
Consider a hypothetical beverage campaign. The bottle photograph is supplied by the client, the surrounding landscape is generated, and the label typography is designed manually. A useful disclosure identifies those parts. Saying only that “AI was used” leaves the client unable to assess what was generated and what must remain accurate to the product.
Inspect the delivered export
Do not assume that a credential present in the working application survives every export, optimization step, content management system, or messaging platform. Download the final delivered asset and inspect that copy. If the public version loses its embedded record, retain the signed original and any available verification reference in the project archive.
Pair the credential with a short handoff note
The note does not need to become a legal essay. It should identify the asset source, significant AI involvement, license location, credential status, and any known gap in the history. This gives the client a usable record even if their normal software does not display the credential.
When the extra step is worth it
Not every rough concept needs a formal provenance workflow. The strongest cases are assets that will circulate beyond the original team, work where AI use could affect approval, commissioned content that needs attribution, and public-facing imagery where origin may later be questioned.
It is also useful when several contributors edit the same asset. A sequence of credentials can create a visible history as compatible tools add new manifests. That record will not capture every action performed in unsupported software, but it can make the supported parts of the chain easier to inspect.
For a private mood board or disposable internal sketch, the administrative cost may outweigh the benefit. Even then, ordinary source notes are still sensible. The decision should reflect the risk and lifespan of the asset, not a belief that every file needs a trust badge.
A practical client-handoff checklist
- Keep the original source asset and proof of its license.
- Inspect any existing Content Credential before editing.
- Record material AI involvement in plain language.
- Apply a credential at final export when the tool and format support it.
- Inspect the exported file rather than trusting the application preview.
- Test the actual file delivered through the chosen platform.
- Send license information separately from provenance information.
- Archive the signed final file, source log, and client approval together.
Content Credentials are useful because they make parts of a creative history inspectable and resistant to unnoticed tampering. Their value disappears when they are treated as a universal certificate of truth or ownership.
Use them as one layer in a responsible design workflow. Keep the original assets, document rights, explain meaningful AI use, and verify the final delivery. That combination gives a client something much stronger than a screenshot or a promise.